From Chaos to Compliance: Building Governance That Actually Scales
About this talk
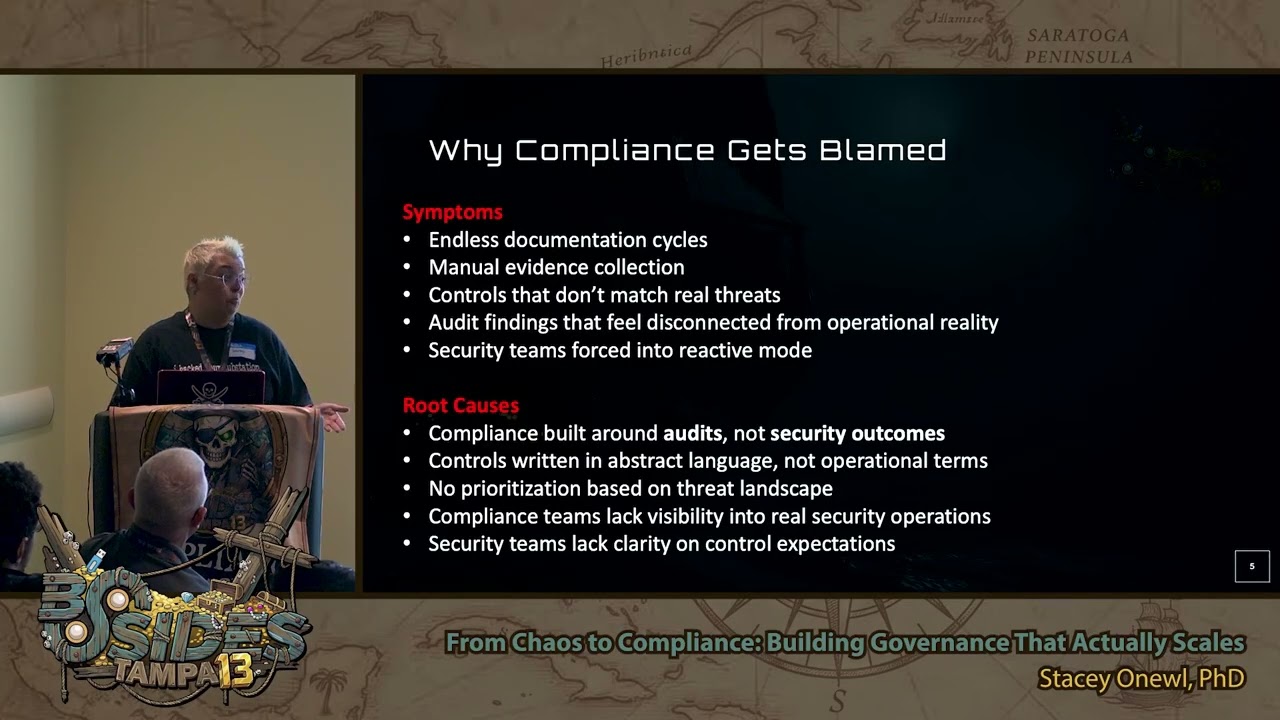
From Chaos to Compliance: Building Governance That Actually Scales by Stacey Onewl, PhD Let’s be honest. In most organizations, compliance is often treated like the annoying hall monitor of cybersecurity; the team everyone loves to blame when innovation slows down, audits go awry, or someone discovers a control gap the size of a small planet. Meanwhile, security engineering is out there building cool things, fighting fires, and wondering why compliance keeps getting in the way. Here’s the plot twist: Compliance isn’t the villain. Bad compliance is. In this talk, I’ll break down how compliance, when done right, becomes the backbone of scalable, defensible, engineering‑aligned security and how, when it’s done wrong, it becomes a bureaucratic nightmare that drags everyone down. Drawing on 15+ years of leading enterprise assurance programs, advising boards, and working shoulder‑to‑shoulder with engineers, I’ll show how to turn compliance from a checkbox chore into a strategic accelerator that actually helps teams ship faster and safer. Expect candor. Expect uncomfortable truths. Expect a few spicy takes about frameworks like FedRAMP , NIST SP 800‑53, CMMC, and PCI DSS. And expect to walk away with a blueprint for making compliance something your engineers don’t roll their eyes at.
Related talks
 47:39
Mastering Android Security Research: A Guide for the Modern Security Researcher
BSides Tampa · 2024
 47:03
Another Round On The Treadmill by @_JohnHammond
BSides Tampa · 2025
 51:22
The No BS SOC Story
BSides Tampa · 2024
 43:03
Social Engineerios: How AI Changes (and Doesn't Change) Social Engineering
BSides Tampa · 2026
 34:47
Weaponizing Vtables: Detection Engineering for Kernel-Space Exploits in macOS by Olivia Gallucci
BSides Tampa
 41:58
The Fault in Our Metrics: Rethinking How We Measure Detection & Response by Allyn Stott
BSides Tampa