From Code to Coverage: A Detection Engineer's Journey Through the LDAP Wilderness - Andrew Schwartz
About this talk
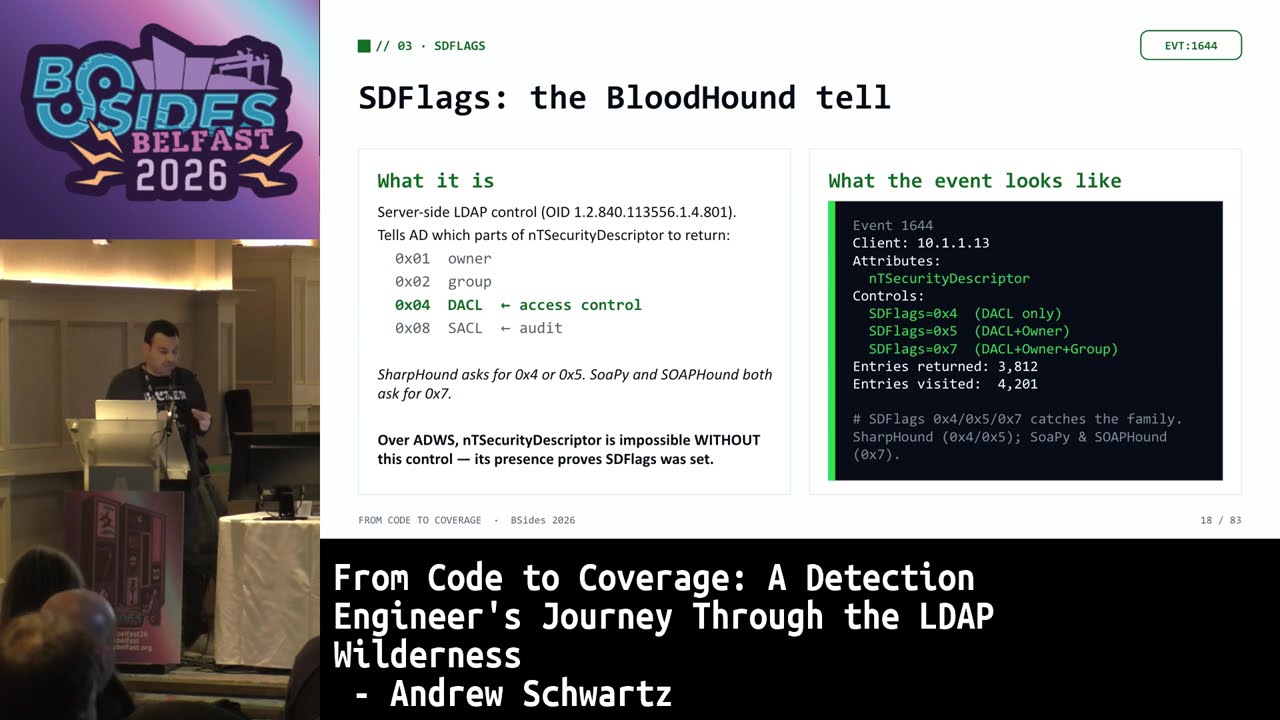
Active Directory reconnaissance tools like BloodHound, Impacket, and SOAPHound are the attacker's first move in enterprise compromises, yet detecting their LDAP queries remains one of the hardest problems in security operations. This talk chronicles a six month journey from writing my first broken Sigma rule to building a complete, evasion resistant LDAP detection stack. You'll learn why traditional signature based detection fails spectacularly, how to think like both an attacker and a parser, and how mathematical approaches can outsmart evasion techniques. We'll cover OID transformations that break your rules, whitespace variations that mock your regex, hidden LDAP parameters that bypass your detections, and ultimately, statistical methods that make evasion mathematically impossible. This isn't theory. Every technique is battle tested in production environments with working Sigma rules, real attack logs, and actual false positive rates. Leave with detection rules you can deploy Monday morning.
Related talks
 36:09
New Attacks On The MIFARE DESFire EV1 Smartcard Used In Public Transportation
BSides Belfast · 2020
 41:29
Demystifying QBot Banking Trojan - Nick Summerlin and Jorge Rodriguez
BSides Belfast · 2020
 44:26
Crowdsourced Security
BSides Belfast · 2018
 14:53
Help Yourself! Exploiting Self-Service Kiosks
BSides Belfast · 2025
 48:41
Offensive Ansible For Red Teams
BSides Belfast · 2020
 26:35
Lazarus On The Rise: Insights From SWIFT Bank Attacks
BSides Belfast · 2018